JobTracker3 · Compliance & GRC

    JobTracker3 Compliance: assets, information security, suppliers and privacy in one software

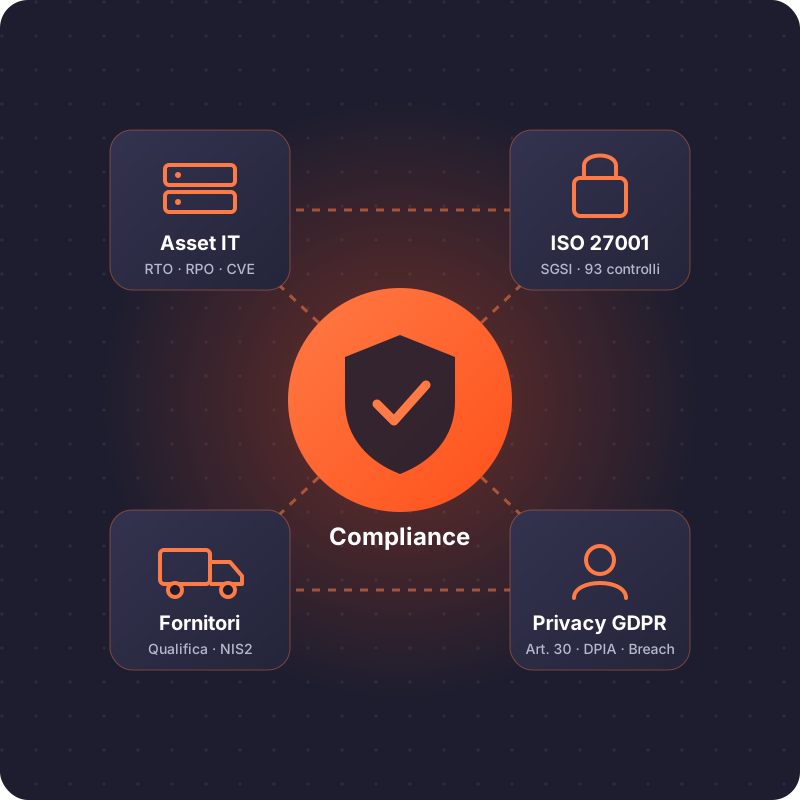
    Four modules built into the JobTracker3 ERP to manage the IT asset inventory, the ISO/IEC 27001 management system, supplier qualification and monitoring, and GDPR obligations. One database, one register of evidence, ready for certification audits, NIS2 assessments and data protection inspections.

    Last updated:

    JobTracker3 Compliance: IT asset management, ISO 27001 ISMS, supplier qualification and GDPR privacy on a single database

    In short

    JobTracker3 Compliance is the GRC (Governance, Risk & Compliance) suite developed by Eulogika S.r.l. of Rubano (Padua, Italy) inside the JobTracker3 ERP. It brings together, in a single on-premise web application, asset and IT infrastructure management, an information security management system aligned with ISO/IEC 27001:2022, supplier qualification and periodic evaluation, and the privacy obligations of the GDPR (EU Regulation 2016/679). It is designed for manufacturing and service SMEs that must demonstrate compliance with ISO 27001, the NIS2 directive and the GDPR without juggling dozens of disconnected spreadsheets.

    Key facts

    Vendor
    Eulogika S.r.l., Italian software house since 2001, ISO/IEC 27001:2022 certified
    Software type
    GRC suite built into the JobTracker3 ERP (web application)
    Modules
    Assets & IT infrastructure · ISO 27001 ISMS · Supplier qualification · GDPR privacy
    Standards covered
    ISO/IEC 27001:2022, ISO/IEC 27002:2022, NIS2 (EU 2022/2555, Italian Legislative Decree 138/2024), GDPR (EU 2016/679), ISO 9001:2015 §8.4
    Deployment
    On-premise or on dedicated infrastructure managed by Eulogika; multi-company
    Technology
    .NET 10, Blazor, SQL Server, OpenAPI REST API
    Application security
    TOTP two-factor authentication, granular permissions on 16 actions, masking of sensitive fields
    Languages
    Italian, English

    Why one system for assets, security, suppliers and privacy

    ISO 27001, NIS2 and the GDPR ask for the same things from different angles: know which assets and data you hold, assess their risks, control who handles them inside and outside the company, and prove it with evidence. When the inventory, the risk register, the supplier list and the record of processing live in separate files, every audit becomes a reconciliation exercise. In JobTracker3 they are linked: the asset points to its risks, the risk to its controls, the supplier to the assets and processing activities entrusted to it.

    A single source of truth

    Assets, risks, suppliers and processing activities share master data and the database with the ERP: no double entry, no conflicting versions.

    Audit-ready evidence

    Every record is dated, attributed to a user and linked to its control: the auditor finds the proof without looking for it.

    Continuous, not annual, compliance

    Deadlines, re-evaluations and scheduled maintenance raise automatic reminders and notifications all year round.

    Permissions on every field

    The DPO sees processing activities, IT sees assets, purchasing sees suppliers: each only what concerns them, with JobTracker3's granular permissions.

    The four JobTracker3 Compliance modules

    Each module is activated independently and works on the same data as the ERP.

    Asset and IT Infrastructure Management

    How do you keep the asset inventory required by ISO 27001 and NIS2?

    The tree-structured asset register records servers, clients, network devices, software, cloud services and information, with owner, location, classification and criticality. Scheduled maintenance carries RTO, RPO and MTD targets; software updates are tracked with the CVE reference of the vulnerability they close; the network inventory is shown as a connection graph.

    Regulatory references
    ISO 27001 A.5.9A.7.13A.8.8A.5.30NIS2 art. 21.2(c)(e)(i)
    • Hierarchical asset register with owner, classification and criticality
    • Scheduled maintenance with RTO, RPO and MTD targets
    • Software updates and patches with CVE references
    • Company network inventory and graph
    • Asset linked to risks, suppliers and personal data processing

    ISO/IEC 27001 Management System

    Which software should you use to run an ISO 27001:2022 ISMS?

    The ISMS module guides the whole management system cycle: context of the organization and interested parties, risk register with assessment and treatment, Statement of Applicability on the 93 Annex A controls, business impact analysis (BIA), incident register, non-conformities and corrective actions, internal audits, management reviews, training plans and a versioned document register.

    Regulatory references
    ISO 27001 §4–10§6.1.2–6.1.3A.5.24–5.28§9.2–9.3NIS2 art. 21.2(a)(b)(g)
    • Context, interested parties and scope
    • Risk register with assessment, treatment and residual risk
    • Statement of Applicability on the 93 ISO/IEC 27001:2022 controls
    • BIA, incidents, non-conformities and corrective actions
    • Internal audits, management reviews, training and document register

    Supplier Qualification and Evaluation

    How do you qualify and monitor suppliers for ISO 27001, NIS2 and ISO 9001?

    The approved supplier list starts from the ERP master data and adds the qualification process: evaluation questionnaires on security, quality and data protection, certificates and documents with expiry dates, score and qualification status, periodic re-evaluation and evaluation history. ICT suppliers and those processing personal data are linked to the assets and processing activities concerned, so the supply chain becomes measurable.

    Regulatory references
    ISO 27001 A.5.19–5.23NIS2 art. 21.2(d)ISO 9001 §8.4GDPR art. 28
    • Approved supplier list linked to master data and purchasing
    • Qualification questionnaires on security, quality and privacy
    • Certificates and documents with expiry dates and reminders
    • Score, qualification status and periodic re-evaluation
    • Map of critical suppliers by assets and processing entrusted

    Privacy and GDPR Compliance

    How do you manage the record of processing, DPIAs and data breaches under the GDPR?

    The privacy module maintains the record of processing activities as controller and as processor, with purposes, legal bases, categories of data and data subjects, recipients, transfers and retention periods. It supports data protection impact assessments (DPIA), the personal data breach register with notification deadlines, data subject requests and the appointment of external processors, linked to the supplier list.

    Regulatory references
    GDPR art. 5, 28, 30art. 32–35art. 15–22ISO 27001 A.5.34
    • Record of processing for controller and processor (art. 30)
    • Data protection impact assessment (DPIA, art. 35)
    • Breach register with 72-hour notification timing (art. 33–34)
    • Data subject requests: access, rectification, erasure (art. 15–22)
    • Processor appointments linked to suppliers (art. 28)

    Regulatory map: which module covers which requirement

    How the requirements of ISO/IEC 27001:2022, the NIS2 directive, the GDPR and ISO 9001 map to JobTracker3 Compliance features.

    Regulatory map: which module covers which requirement
    RequirementReferenceJobTracker3 module
    Inventory of information and assetsISO 27001 A.5.9 · NIS2 art. 21.2(i)Assets & IT infrastructure
    Technical vulnerability managementISO 27001 A.8.8 · NIS2 art. 21.2(e)Assets & IT infrastructure
    Business continuity, backup and recoveryISO 27001 A.5.30, A.8.13 · NIS2 art. 21.2(c)Assets (RTO/RPO/MTD) · ISMS (BIA)
    Risk assessment and treatmentISO 27001 §6.1.2–6.1.3 · NIS2 art. 21.2(a)ISO 27001 ISMS
    Statement of ApplicabilityISO 27001 §6.1.3 d)ISO 27001 ISMS
    Incident managementISO 27001 A.5.24–5.28 · NIS2 art. 21.2(b), art. 23ISO 27001 ISMS
    Training and awarenessISO 27001 A.6.3 · NIS2 art. 21.2(g)ISO 27001 ISMS
    Internal audit and management reviewISO 27001 §9.2–9.3ISO 27001 ISMS
    Supply chain securityISO 27001 A.5.19–5.22 · NIS2 art. 21.2(d)Supplier qualification
    Control of external providersISO 9001 §8.4Supplier qualification
    Data processorsGDPR art. 28Privacy · Supplier qualification
    Record of processing activitiesGDPR art. 30GDPR privacy
    Personal data breach notificationGDPR art. 33–34GDPR privacy · ISMS (incidents)
    Data protection impact assessmentGDPR art. 35GDPR privacy
    Privacy and protection of PIIISO 27001 A.5.34GDPR privacy

    How the four modules work together

    1. 01

      Inventory

      Record assets, information and personal data processing, each with its owner.

    2. 02

      Assess

      Link each asset to its risks, calculate residual risk and decide controls in the Statement of Applicability.

    3. 03

      Qualify

      Evaluate the suppliers that touch assets and data, collect certificates and appoint processors.

    4. 04

      Monitor

      Maintenance, CVE patches, incidents and breaches are recorded and notified within the required time.

    5. 05

      Demonstrate

      Internal audits and reviews find evidence already linked to requirements and controls.

    Spreadsheets or JobTracker3 Compliance?

    Spreadsheets or JobTracker3 Compliance?
    AspectScattered spreadsheets and documentsJobTracker3 Compliance
    Links between assets, risks, suppliers and processingManual, by text referencesNative relations in the same database
    Certificate, maintenance and re-evaluation deadlinesPersonal calendarsAutomatic reminders and notifications
    Who changed whatMissing or partialEvery record dated and attributed
    Access controlShared foldersGranular permissions by role, company and field
    Audit preparationDays of collection and reconciliationEvidence already linked to controls
    Supplier dataCopied from the ERPThe ERP's own master data

    Who JobTracker3 Compliance is for

    NIS2 entities

    Essential and important entities that must apply the measures of article 21 and document them for the national cybersecurity authority.

    ISO 27001 certified companies

    Organizations that want to keep their ISMS alive all year, not just the week before the audit.

    Manufacturing SMEs with an extended supply chain

    Companies that must qualify suppliers and subcontractors for their own customers and for ISO 9001.

    DPOs, consultants and IT managers

    Those who manage privacy and security for one or more companies of the same group, with a single multi-company installation.

    Built by people who apply ISO 27001 every day

    Eulogika is a software house based in Rubano (Padua, Italy), operating since 2001 and certified ISO/IEC 27001:2022. JobTracker3's compliance modules come from our own management system and from the NIS2 and GDPR projects we run for industrial customers: they are the tool we use, not a theoretical exercise.

    4
    GRC modules on a single database
    93
    Annex A controls in the Statement of Applicability
    2001
    year Eulogika was founded

    Frequently asked questions about JobTracker3 Compliance

    What is JobTracker3 Compliance?

    JobTracker3 Compliance is the set of GRC modules of Eulogika's JobTracker3 ERP: asset and IT infrastructure management, an ISO/IEC 27001:2022 information security management system, supplier qualification and evaluation, and GDPR privacy obligations. It runs as an on-premise web application on the same database as the ERP.

    Does JobTracker3 help achieve ISO 27001 certification?

    Yes. The ISMS module covers the requirements of clauses 4–10 of ISO/IEC 27001:2022 and the Statement of Applicability on the 93 Annex A controls, with risk register, incidents, non-conformities, internal audits, reviews and training. Certification is still issued by an accredited body: JobTracker3 organizes the evidence the auditor checks.

    Is JobTracker3 useful for NIS2 compliance?

    Yes. The risk management measures of article 21 of the NIS2 directive map to the modules: risk analysis, incident handling, business continuity, supply chain security, vulnerability handling, training and asset management. Two-factor authentication is native to the application.

    How does JobTracker3 handle supplier qualification?

    The approved supplier list starts from the ERP master data and adds qualification questionnaires on security, quality and privacy, certificates with expiry dates, score, qualification status and periodic re-evaluation. It is aligned with ISO 27001 controls A.5.19–5.22, NIS2 article 21.2(d) and ISO 9001 §8.4.

    Does the privacy module replace the DPO?

    No. The privacy module is the tool controllers, processors and DPOs use to keep the record of processing, DPIAs, the breach register and data subject requests. Legal assessments remain with the competent people; JobTracker3 keeps their decisions and deadlines.

    How are personal data breaches handled?

    Each breach is recorded with discovery date, nature, categories and approximate number of data subjects, consequences and measures taken. The system highlights the 72-hour deadline for notifying the supervisory authority under GDPR article 33 and can be linked to the security incident recorded in the ISMS.

    Can I activate only some modules?

    Yes. Every JobTracker3 module is activated independently: you can start with the asset inventory or supplier qualification and add the ISMS and privacy later, with no migration.

    Do I need to use the whole JobTracker3 ERP?

    No. The compliance modules can be used without accounting, sales or production: JobTracker3 then provides master data, users, permissions and notifications. If the ERP is already in use, suppliers and assets are the same as in the ERP.

    Where is the data stored?

    On the company's own servers with an on-premise installation, or on dedicated infrastructure managed by Eulogika. Each customer has its own installation; several companies of the same group can coexist with data isolation guaranteed by design.

    How long does it take to get started?

    It depends on the starting point. A typical project begins by importing the inventories, registers and supplier lists already kept in Excel, configures roles and permissions and activates modules in phases. Eulogika analyzes the processes and proposes a plan before starting.

    Bring compliance into your ERP

    We'll show you JobTracker3 Compliance on your own assets, suppliers and processing activities, starting from the registers you use today.